Privacy Policy
1. Purpose and scope
This Privacy Policy explains how SITASC LTD. processes personal data in connection with the Website, inquiries, requests for quotations and related B2B communications. GDPR (General Data Protection Regulation) requires information about processing to be concise, transparent, understandable and accessible, including information about purposes, legal bases, recipients, retention and individual rights.
2. Data controller
The controller of personal data is SITASC LTD., legal entity identified in the Website footer or Contact page, including its registered name, address and company-registration details. Data-protection requests may be submitted using the privacy contact details published on the Contact page. If SITASC LTD. appoints a Data Protection Officer, the Officer’s contact details will be added to this Policy.
3. Data collected
Depending on how the Website is used, SITASC LTD. may process:
· Identity and professional data: name, surname, job title, department, employer and authority to represent an organisation;
· Contact data: business email address, telephone number, postal address and preferred language;
· Inquiry and project data: message content, requested products or services, specifications, site and application information, attachments, quotation history and correspondence;
· Technical data: IP address, browser and device information, operating system, timestamps, requested resources, referring page, error records and security logs;
· Consent and preference data: cookie choices, marketing preferences and records demonstrating when and how a choice was made;
· Business relationship data: meeting notes, quotation status and information necessary to establish, manage or defend a potential or existing contractual relationship.
Business contact details relating to identifiable employees, directors, representatives and other contact persons are personal data protected by GDPR.
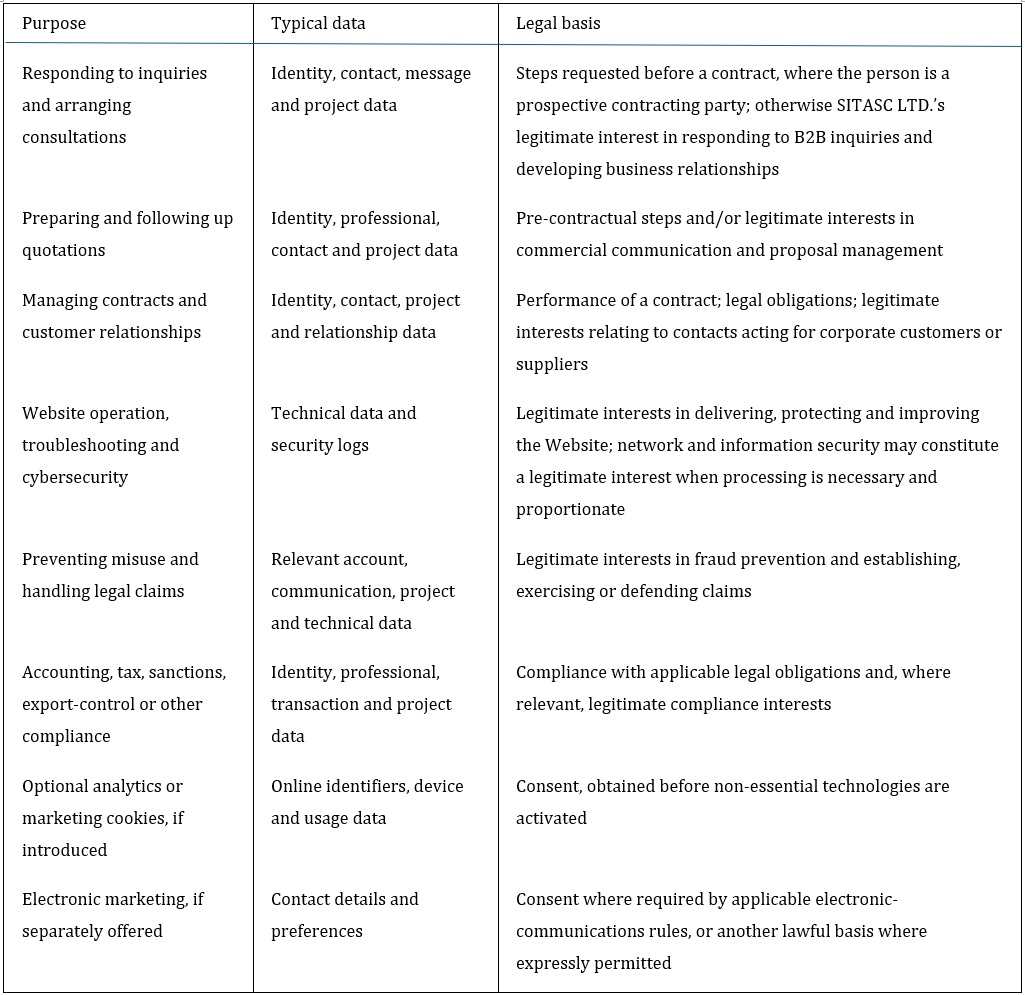
4. Purposes and legal bases
Personal data are processed only where an appropriate legal basis applies. GDPR recognises, among other grounds, consent, steps requested before a contract, performance of a contract, compliance with a legal obligation and legitimate interests not overridden by the person’s rights.
Where processing relies on legitimate interests, SITASC LTD. considers the purpose, necessity and impact on the person concerned. A person may object as explained below.
5. How data are obtained
SITASC LTD. normally obtains personal data directly from the person through a form, email, telephone call, meeting or other communication. Data may also be received from the person’s employer or colleague, a project partner, manufacturer, distributor, publicly available professional source or corporate website where relevant to a legitimate B2B relationship. When data are collected directly, transparency information should be provided at collection; where data are obtained indirectly, GDPR timing rules also apply.
6. Required information
Providing data is voluntary unless required by law or contract. However, SITASC LTD. may be unable to answer an inquiry, prepare a reliable technical proposal or proceed with a project if the necessary contact, application or specification data are not provided. Users should provide only data relevant to the inquiry and should not submit special-category personal data or unnecessary private information.
7. Recipients
Personal data may be disclosed, only where necessary, to:
· authorised SITASC LTD. personnel and entities supporting the relevant inquiry or project;
· European hosting, cloud, email, cybersecurity, IT-support, CRM and backup providers acting under appropriate contractual controls;
· professional advisers, auditors and insurers;
· manufacturers, engineering partners, logistics providers, service partners or subcontractors where necessary to assess or fulfil a request and where a lawful basis applies;
· public authorities, courts or law-enforcement bodies where disclosure is legally required;
· parties involved in a corporate restructuring, subject to lawful safeguards.
GDPR transparency information must identify recipients or categories of recipients, and users must be informed when their information will be shared with third parties.
8. European data storage
All personal data collected through this Website are stored on servers located in Europe, within the European Economic Area (EEA). SITASC LTD. selects Website hosting, email, database and backup services configured for European data residency. SITASC LTD. does not intentionally transfer Website personal data outside the EEA. Remote access from, or disclosure to a recipient in, a country outside the EEA will not be permitted unless it is necessary, this Policy is updated where required, and the transfer complies with GDPR Chapter V—for example, through an adequacy decision or appropriate safeguards and enforceable rights. European server location alone does not prevent an international transfer if a non-EEA recipient can remotely access personal data. Accordingly, SITASC LTD. must verify vendor support access, subcontractors, backups, telemetry and the access rights of personnel before retaining this statement.
9. Retention
SITASC LTD. retains personal data only for as long as necessary for the relevant purpose, applying the following working periods:
· Unsuccessful or closed inquiries and quotation requests: up to 24 months after the final substantive communication, unless a longer period is justified by renewed negotiations or a legal claim;
· Customer, supplier and contract records: for the duration of the relationship and then for the periods required by tax, accounting, warranty, compliance and limitation laws;
· Website security and server logs: normally up to 12 months, with longer retention where needed to investigate an incident, prevent abuse or establish a claim;
· Consent and preference records: for as long as the relevant processing continues and afterwards as necessary to demonstrate compliance or address claims;
· Cookie data: for the lifetime stated in the Website’s live cookie settings or consent panel.
Data may be deleted, anonymised or retained for longer where law requires it or where necessary to establish, exercise or defend legal claims. GDPR requires the notice to state the retention period or, where that is not possible, the criteria used to determine it.
10. Individual rights
Subject to the conditions and exceptions in applicable law, a person may request:
· access to their personal data and a copy of the data;
· correction of inaccurate or incomplete data;
· erasure of personal data;
· restriction of processing;
· data portability where processing is based on consent or contract and carried out by automated means;
· objection to processing based on legitimate interests;
· withdrawal of consent at any time, without affecting processing carried out before withdrawal;
· information about applicable safeguards for an international transfer.
Requests may be made through the privacy contact details published on the Website. SITASC LTD. may request information reasonably necessary to verify identity and should respond without undue delay, normally within one month as required by GDPR. A person also has the right to lodge a complaint with the competent supervisory authority. This is generally the The Office of the Privacy Commissioner for Personal Data (PCPD) in Hong Kong. The privacy notice must communicate the right to complain, but it is not legally necessary to reproduce the authority’s complete address in the notice.
11. Automated decisions
SITASC LTD. does not use Website data to make decisions based solely on automated processing that produce legal effects or similarly significant effects on individuals. If this changes, this Policy will be updated and the required information and safeguards will be provided.
12. Security
SITASC LTD. applies technical and organisational measures appropriate to the nature of the data and processing risks. These may include access controls, least-privilege permissions, encryption in transit, system updates, backups, logging, incident procedures, vendor controls and staff confidentiality obligations. No internet transmission or storage system can be guaranteed completely secure. Users should avoid sending confidential engineering or commercially sensitive information through an unsecured general contact channel.
13. Cookies
Cookies are small files or identifiers stored on or accessed from a user’s device. They may contain personal data such as an IP address, username or unique identifier. The Website is assumed to use only cookies and similar technologies strictly necessary for functions requested by the user, security, load balancing, form operation and storage of privacy choices. These technologies do not require consent where they are strictly necessary, but users must receive clear information about them. If SITASC LTD. adds analytics, advertising, social-media pixels, embedded media or other non-essential technologies, they must remain disabled until the user gives freely given, specific, informed and unambiguous consent. The consent tool should offer a genuine accept/reject choice, identify purposes and relevant third parties, state cookie duration, and permit consent withdrawal as easily as it was given. A live cookie list should be generated from the technologies actually deployed and made accessible through a persistent “Cookie settings” link. Browser controls may also delete or block cookies, but blocking strictly necessary technologies can affect Website functions.
14. External services
Following links to external websites or activating third-party content may allow the third party to process personal data under its own policy. SITASC LTD. should configure embedded maps, videos, social-media widgets and similar services so they do not load non-essential trackers before consent.
15. Children
The Website is intended for professional and business users and is not directed at children. SITASC LTD. does not knowingly seek personal data from children through the Website.
16. Policy changes
SITASC LTD. may update this Privacy Policy when its processing, vendors, Website functions or legal obligations change. Material changes will be highlighted where appropriate, and the latest revision date will appear at the top of the Policy. Transparency information should be updated when the controller, purpose or method for exercising rights changes.
17. Privacy contact
Privacy questions and rights requests may be submitted using the official email address, contact form or registered postal address shown on the Website’s Contact page. The request should be marked “Data Protection Request” to support efficient handling.